 By lampliter
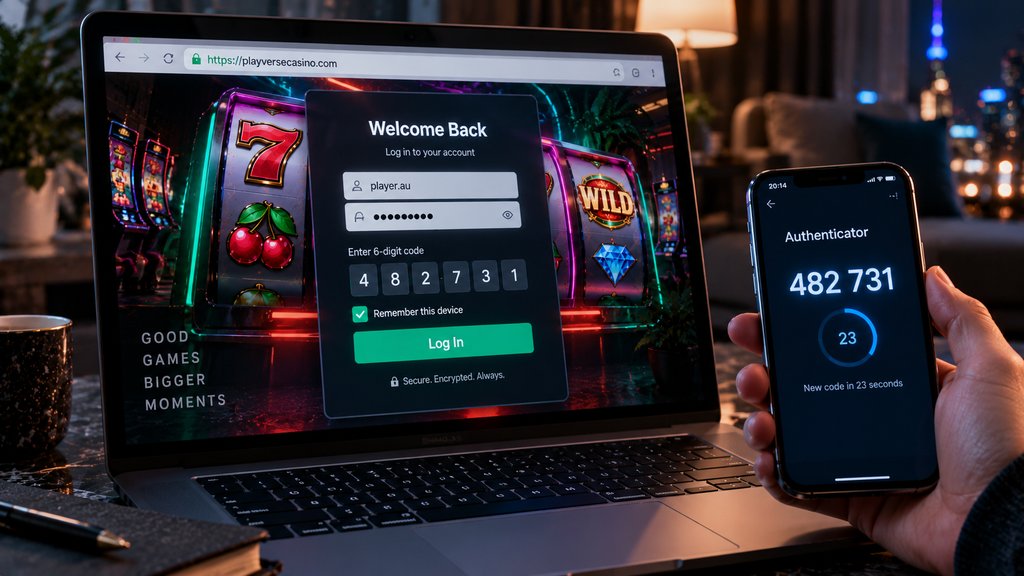
An online casino account can contain personal details, payment history and a cash balance, making basic security worthwhile before any deposit is made. The Leon Casino login and account security setup shows Australian players what the official sign-in process looks like and how to recognise it on the correct page.
Account protection is built from several small habits. A unique password reduces exposure from breaches elsewhere, multi-factor authentication adds a second check, and careful device use limits opportunities for another person to access an active session.
Use a unique password for the casino
Reusing a password across email, shopping and casino accounts creates a chain of exposure. If one service is breached, automated login attempts can test the same credentials elsewhere.
A strong password should be long and unrelated to public personal information. A password manager such as Bitwarden or 1Password can generate and store a different value for every service, removing the need to remember complex strings.
The casino password is especially important because the linked email account often controls resets. Both accounts should use separate passwords.
Protect the email account first
Password-reset links and security notices are normally sent by email. Someone who controls the inbox may be able to change the casino login even without knowing the original password.
The email account should use its own MFA and current recovery information. Old phone numbers and unused backup addresses should be removed.
Security alerts should be reviewed promptly. A reset email the player did not request is a signal to review account activity immediately.
Enable MFA when available
Multi-factor authentication requires another proof after the password, such as an authenticator code, device prompt or one-time message.
Authenticator apps such as Google Authenticator or Authy generate time-based codes that refresh every 30 seconds. These are generally more reliable than intercepted text messages, though the casino may support only selected methods. Backup codes should be stored offline, separate from the device that generates them.
MFA adds another barrier when a password is exposed. Both layers work together.
Check the website before signing in
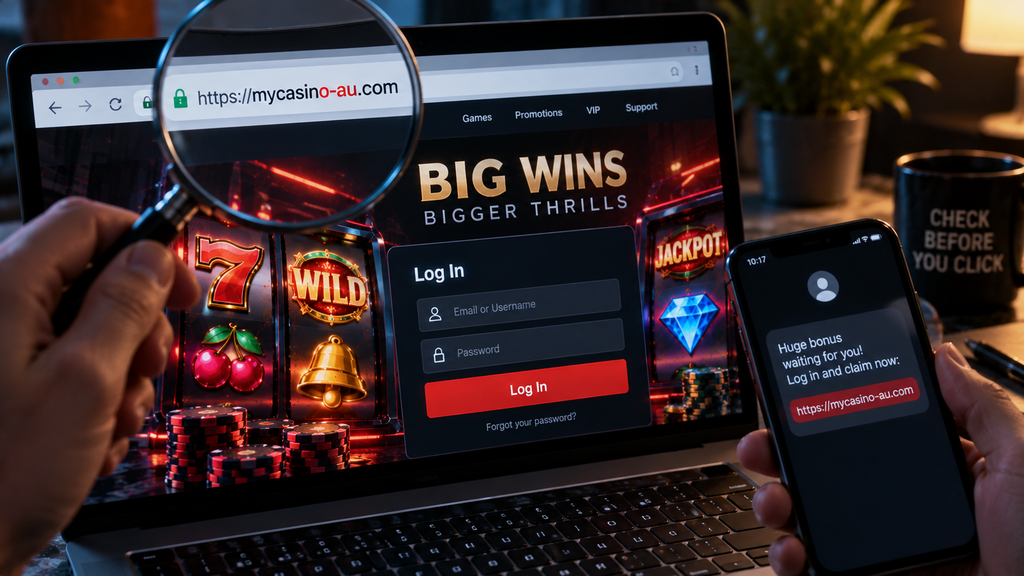
Phishing sites can copy a casino’s design and login form closely. Players should check the web address before entering account details and use a saved official bookmark when possible.
Warning signs include extra words or characters in the domain, altered spelling and an unexpected domain extension. HTTPS and a padlock indicate an encrypted connection, but do not by themselves prove that the site is legitimate.
Opening the casino from a verified bookmark is safer than following login links received by email, text message or other messages.
Keep devices updated
Operating-system, browser and security updates correct known weaknesses. Delaying them can leave a phone or computer exposed to issues already addressed by the manufacturer.
Apps should come from official stores or confirmed casino sources. Modified software and unknown browser extensions can capture login information.
A screen lock with a PIN, password or biometric check protects the account if the device is misplaced.
Avoid shared and public devices
A public computer may save browser data or contain monitoring software. Shared household devices can also expose an active session if the player forgets to log out.
If a shared device is the only option, credentials should be entered fresh each time and the session closed completely afterward. Private browsing reduces local history but leaves the underlying device environment unchanged.
A trusted mobile connection is usually the clearer option for payments and account changes on public networks.
Review login and payment notifications
Some casinos show recent sessions, device information or transaction alerts. Players can compare these records with their own activity.
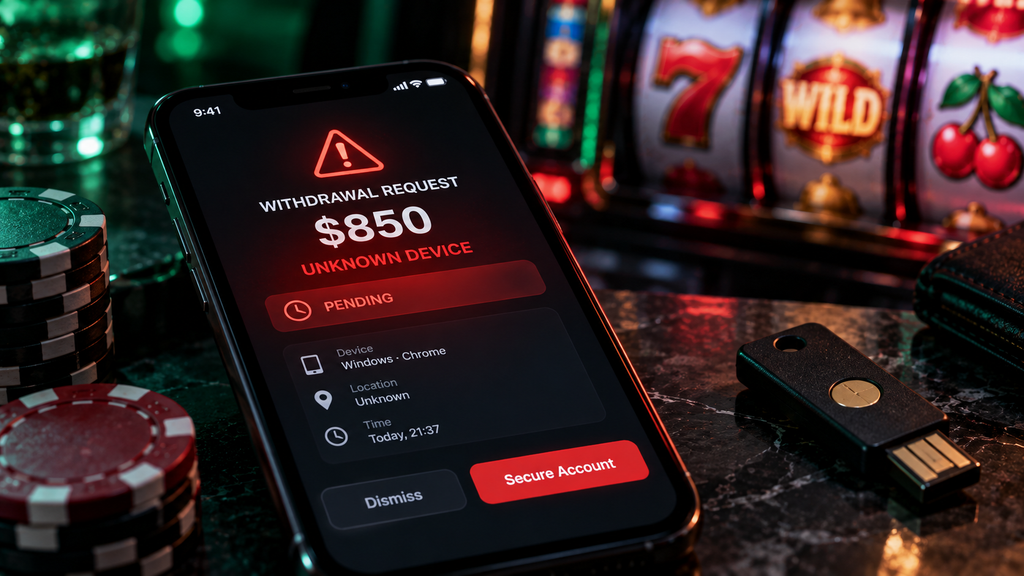
Unrecognised deposits, password changes or withdrawal attempts deserve immediate attention. Small unknown transactions can be early signs of account testing before a larger request.
Payment providers can also send alerts. Keeping those notifications active adds another independent record.
Secure documents used for verification
Identity files should be uploaded only through the official account area or an address confirmed by support. Documents sent through public social-media messages carry a higher exposure risk.
Copies stored on a device can contain full names, addresses and document numbers. Moving them to protected storage or removing them when the verification is complete reduces ongoing exposure.
If a card image is requested, the casino’s instructions explain which digits and security details to cover.
Log out and manage sessions
The account’s log-out control should be used after each visit, especially on any device accessed by other people. Closing a browser tab leaves the session active on many platforms.
Some services allow players to end all active sessions after a password change. This is useful if a phone is misplaced or an unknown device appears in the session list.
Automatic login is convenient on a personal device but carries more risk on a shared one.
Respond quickly to suspicious activity
If the account may be compromised, changing the email password first, then the casino password, and enabling or resetting MFA covers the main entry points. Support can restrict withdrawals while the activity is reviewed.
A useful report includes the time of the unknown event, transaction amount, device details and any messages received. Payment providers should be contacted separately if card or bank information may be involved.
| Warning sign | Immediate action |
| Unknown password-reset email | Secure email and casino passwords |
| New device alert | End sessions and review activity |
| Unrecognised withdrawal | Contact casino support immediately |
| Lost phone | Lock device and revoke sessions |
| Phishing message opened | Change credentials from a trusted device |
Screenshots and reference numbers should be retained until the issue is resolved.
Keep recovery information current
An account can become harder to recover when the registered phone or email is no longer in use. Contact details should be updated through the official verification process before that situation arises.
Security questions, if used, work better with stored random answers than with factual details that another person can research from social media.
Australian players who use unique passwords, protect their email, activate MFA and keep devices controlled have a clear plan for both everyday security and responding to unusual activity.